OnionDuke Samples

quinta-feira, 1 de junho de 2023


File attributes

Size: 219136
MD5:  28F96A57FA5FF663926E9BAD51A1D0CB

Size: 126464
MD5:  C8EB6040FD02D77660D19057A38FF769


Size: 316928
MD5:  D1CE79089578DA2D41F1AD901F7B1014


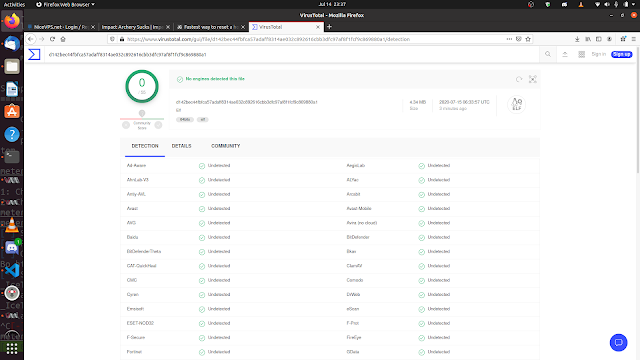
Virustotal info

https://www.virustotal.com/en/file/366affd094cc63e2c19c5d57a6866b487889dab5d1b07c084fff94262d8a390b/analysis/
SHA256: 366affd094cc63e2c19c5d57a6866b487889dab5d1b07c084fff94262d8a390b
File name: 366affd094cc63e2c19c5d57a6866b487889dab5d1b07c084fff94262d8a390b
Detection ratio: 8 / 52
Analysis date: 2014-11-15 18:37:30 UTC ( 8 hours, 44 minutes ago ) 
Antivirus Result Update
Baidu-International Trojan.Win32.Agent.adYf 20141107
F-Secure Backdoor:W32/OnionDuke.B 20141115
Ikarus Trojan.Win32.Agent 20141115
Kaspersky Backdoor.Win32.MiniDuke.x 20141115
Norman OnionDuke.A 20141115
Sophos Troj/Ransom-ALA 20141115
Symantec Backdoor.Miniduke!gen4 20141115
Tencent Win32.Trojan.Agent.Tbsl 20141115

https://www.virustotal.com/en/file/366affd094cc63e2c19c5d57a6866b487889dab5d1b07c084fff94262d8a390b/analysis/


SHA256: 366affd094cc63e2c19c5d57a6866b487889dab5d1b07c084fff94262d8a390b
File name: 366affd094cc63e2c19c5d57a6866b487889dab5d1b07c084fff94262d8a390b
Detection ratio: 8 / 52
Antivirus Result Update
Baidu-International Trojan.Win32.Agent.adYf 20141107
F-Secure Backdoor:W32/OnionDuke.B 20141115
Ikarus Trojan.Win32.Agent 20141115
Kaspersky Backdoor.Win32.MiniDuke.x 20141115
Norman OnionDuke.A 20141115
Sophos Troj/Ransom-ALA 20141115
Symantec Backdoor.Miniduke!gen4 20141115
Tencent Win32.Trojan.Agent.Tbsl 20141115

https://www.virustotal.com/en/file/0102777ec0357655c4313419be3a15c4ca17c4f9cb4a440bfb16195239905ade/analysis/
SHA256: 0102777ec0357655c4313419be3a15c4ca17c4f9cb4a440bfb16195239905ade
File name: 0102777ec0357655c4313419be3a15c4ca17c4f9cb4a440bfb16195239905ade
Detection ratio: 19 / 55
Analysis date: 2014-11-15 18:37:25 UTC ( 8 hours, 47 minutes ago ) 
Antivirus Result Update
AVware Trojan.Win32.Generic!BT 20141115
Ad-Aware Backdoor.Generic.933739 20141115
Baidu-International Trojan.Win32.OnionDuke.BA 20141107
BitDefender Backdoor.Generic.933739 20141115
ESET-NOD32 a variant of Win32/OnionDuke.A 20141115
Emsisoft Backdoor.Generic.933739 (B) 20141115
F-Secure Backdoor:W32/OnionDuke.A 20141115
GData Backdoor.Generic.933739 20141115
Ikarus Trojan.Win32.Onionduke 20141115
Kaspersky Backdoor.Win32.MiniDuke.x 20141115
McAfee RDN/Generic BackDoor!zw 20141115
McAfee-GW-Edition BehavesLike.Win32.Trojan.fh 20141114
MicroWorld-eScan Backdoor.Generic.933739 20141115
Norman OnionDuke.B 20141115
Sophos Troj/Ransom-ANU 20141115
Symantec Backdoor.Miniduke!gen4 20141115
TrendMicro BKDR_ONIONDUKE.AD 20141115
TrendMicro-HouseCall BKDR_ONIONDUKE.AD 20141115
VIPRE Trojan.Win32.Generic!BT 20141115


More information


Defcon 2015 Coding Skillz 1 Writeup

Just connecting to the service, a 64bit cpu registers dump is received, and so does several binary code as you can see:


The registers represent an initial cpu state, and we have to reply with the registers result of the binary code execution. This must be automated becouse of the 10 seconds server socket timeout.

The exploit is quite simple, we have to set the cpu registers to this values, execute the code and get resulting registers.

In python we created two structures for the initial state and the ending state.

cpuRegs = {'rax':'','rbx':'','rcx':'','rdx':'','rsi':'','rdi':'','r8':'','r9':'','r10':'','r11':'','r12':'','r13':'','r14':'','r15':''}
finalRegs = {'rax':'','rbx':'','rcx':'','rdx':'','rsi':'','rdi':'','r8':'','r9':'','r10':'','r11':'','r12':'','r13':'','r14':'','r15':''}

We inject at the beginning several movs for setting the initial state:

for r in cpuRegs.keys():
    code.append('mov %s, %s' % (r, cpuRegs[r]))

The 64bit compilation of the movs and the binary code, but changing the last ret instruction by a sigtrap "int 3"
We compile with nasm in this way:

os.popen('nasm -f elf64 code.asm')
os.popen('ld -o code code.o ')

And use GDB to execute the code until the sigtrap, and then get the registers

fd = os.popen("gdb code -ex 'r' -ex 'i r' -ex 'quit'",'r')
for l in fd.readlines():
    for x in finalRegs.keys():
           ...

We just parse the registers and send the to the server in the same format, and got the key.


The code:

from libcookie import *
from asm import *
import os
import sys

host = 'catwestern_631d7907670909fc4df2defc13f2057c.quals.shallweplayaga.me'
port = 9999

cpuRegs = {'rax':'','rbx':'','rcx':'','rdx':'','rsi':'','rdi':'','r8':'','r9':'','r10':'','r11':'','r12':'','r13':'','r14':'','r15':''}
finalRegs = {'rax':'','rbx':'','rcx':'','rdx':'','rsi':'','rdi':'','r8':'','r9':'','r10':'','r11':'','r12':'','r13':'','r14':'','r15':''}
fregs = 15

s = Sock(TCP)
s.timeout = 999
s.connect(host,port)

data = s.readUntil('bytes:')


#data = s.read(sz)
#data = s.readAll()

sz = 0

for r in data.split('\n'):
    for rk in cpuRegs.keys():
        if r.startswith(rk):
            cpuRegs[rk] = r.split('=')[1]

    if 'bytes' in r:
        sz = int(r.split(' ')[3])


binary = data[-sz:]
code = []

print '[',binary,']'
print 'given size:',sz,'bin size:',len(binary)        
print cpuRegs


for r in cpuRegs.keys():
    code.append('mov %s, %s' % (r, cpuRegs[r]))


#print code

fd = open('code.asm','w')
fd.write('\n'.join(code)+'\n')
fd.close()
Capstone().dump('x86','64',binary,'code.asm')

print 'Compilando ...'
os.popen('nasm -f elf64 code.asm')
os.popen('ld -o code code.o ')

print 'Ejecutando ...'
fd = os.popen("gdb code -ex 'r' -ex 'i r' -ex 'quit'",'r')
for l in fd.readlines():
    for x in finalRegs.keys():
        if x in l:
            l = l.replace('\t',' ')
            try:
                i = 12
                spl = l.split(' ')
                if spl[i] == '':
                    i+=1
                print 'reg: ',x
                finalRegs[x] = l.split(' ')[i].split('\t')[0]
            except:
                print 'err: '+l
            fregs -= 1
            if fregs == 0:
                #print 'sending regs ...'
                #print finalRegs
                
                buff = []
                for k in finalRegs.keys():
                    buff.append('%s=%s' % (k,finalRegs[k]))


                print '\n'.join(buff)+'\n'

                print s.readAll()
                s.write('\n'.join(buff)+'\n\n\n')
                print 'waiting flag ....'
                print s.readAll()

                print '----- yeah? -----'
                s.close()


fd.close()
s.close()


Continue reading
  1. Pentest Reporting Tools
  2. Pentest Box Tools Download
  3. Hak5 Tools
  4. Hack Tools Online
  5. New Hacker Tools
  6. New Hacker Tools
  7. Hacking Apps
  8. Pentest Tools For Windows
  9. Hacker Tools For Pc
  10. Pentest Tools Url Fuzzer
  11. Hacker Tools Mac
  12. Best Hacking Tools 2019
  13. Hacking Tools Pc
  14. Hack App
  15. Pentest Tools Website
  16. Pentest Tools Download
  17. Hack Tools For Ubuntu
  18. Hacking Tools Online
  19. Hacking Tools Github
  20. Pentest Tools For Windows
  21. Wifi Hacker Tools For Windows
  22. Pentest Tools Free
  23. Hacker Tools For Mac
  24. Pentest Recon Tools
  25. Github Hacking Tools
  26. Hacking App
  27. Pentest Tools Free
  28. Github Hacking Tools
  29. Hacking Tools Pc
  30. Hacking Tools Online
  31. Pentest Tools Tcp Port Scanner
  32. Pentest Tools Subdomain
  33. Hacking Tools Name
  34. Pentest Tools Port Scanner
  35. Hacker Security Tools
  36. Hacker Tools 2019
  37. Hacker Tools 2020
  38. Hacking Apps
  39. Hacker Tools Mac
  40. Pentest Tools
  41. Pentest Tools Open Source
  42. Pentest Tools Android
  43. New Hack Tools
  44. Hacker Tools Free
  45. Hack Tools
  46. Hacker Tools Hardware
  47. Pentest Tools Download
  48. Kik Hack Tools
  49. Hack Tool Apk No Root
  50. Hack Tools
  51. Tools 4 Hack
  52. Hacking Tools Kit
  53. Pentest Tools Review
  54. Black Hat Hacker Tools
  55. Beginner Hacker Tools
  56. Github Hacking Tools
  57. Hacking Tools Windows
  58. Android Hack Tools Github
  59. Hacker Tools Apk Download
  60. How To Hack
  61. Underground Hacker Sites
  62. Pentest Tools Windows
  63. World No 1 Hacker Software
  64. Hacking Tools 2020
  65. Hack Website Online Tool
  66. Hacker Hardware Tools
  67. Hacker Security Tools
  68. Pentest Reporting Tools
  69. Hacking Apps
  70. Hacking Tools 2020
  71. Nsa Hack Tools Download
  72. Hacker Tools For Ios
  73. Hack Apps
  74. Pentest Tools For Mac
  75. Hacking Tools Mac
  76. Hacking Tools Github
  77. Hacking Tools For Games
  78. Pentest Tools Url Fuzzer
  79. Blackhat Hacker Tools
  80. Pentest Tools Alternative
  81. Pentest Tools Online
  82. Hack Tools 2019
  83. Hacking Tools For Games
  84. Best Hacking Tools 2019
  85. Pentest Tools Subdomain
  86. Hacker
  87. Pentest Tools Open Source
  88. Pentest Tools Apk
  89. Pentest Tools Tcp Port Scanner
  90. New Hacker Tools
  91. Pentest Tools Subdomain
  92. Hacker Tools Apk
  93. Hacking Tools 2020
  94. Hacker Tools Apk Download
  95. Hacking Tools Windows
  96. Hack Tools Download
  97. Hack Tool Apk
  98. Android Hack Tools Github
  99. Bluetooth Hacking Tools Kali
  100. Best Pentesting Tools 2018
  101. Pentest Tools Alternative
  102. Install Pentest Tools Ubuntu
  103. Hack App
  104. Pentest Tools
  105. Hacking App
  106. Hacker Tools Software
  107. Hacking Tools Online
  108. Hacker Tools Free Download
  109. Pentest Tools Apk
  110. Pentest Reporting Tools
  111. Hacker Tools
  112. Hacking Tools Kit
  113. Github Hacking Tools
  114. Pentest Tools Bluekeep
  115. Pentest Tools For Ubuntu
  116. Hacker Techniques Tools And Incident Handling
  117. Hack Tools Pc
  118. Underground Hacker Sites
  119. Pentest Reporting Tools
  120. Top Pentest Tools
  121. Hacker Tools Software
  122. Hacking Tools Hardware
  123. Hacks And Tools
  124. Hack Tools
  125. Tools 4 Hack
  126. Pentest Tools Download
  127. Hack Tools Github

EXOCET - AV-evading, Undetectable, Payload Delivery Tool


EXOCET is superior to Metasploit's "Evasive Payloads" modules as EXOCET uses AES-256 in GCM Mode (Galois/Counter Mode). Metasploit's Evasion Payloads uses a easy to detect RC4 encryption. While RC4 can decrypt faster, AES-256 is much more difficult to ascertain the intent of the malware.


However, it is possible to use Metasploit to build a Evasive Payload, and then chain that with EXOCET. So EXOCET will decrypt via AES-256, and then the Metasploit Evasive Payload then decrypts itself from RC4.

Much like my previous project, DarkLordObama, this toolkit is designed to be a delivery/launch vehicle, much like Veil-Evasion does.

Dark Lord Obama Project

However, EXOCET is not limited to a single codebase or platforms that are running Python. EXOCET works on ALL supported platforms and architectures that Go supports.


Exocet Overview

EXOCET, is effectively a crypter-type malware dropper that can recycle easily detectable payloads like WannaCry, encrypt them using AES-GCM (Galois/Counter Mode), which is more secure than AES-CBC, and then create a dropper file for a majority of architectures and platforms out there.

Basically...

  1. It ingests dangerous malware that are now detectable by antivirus engines
  2. It then encrypts them and produces it's own Go file
  3. Then that Go file can be cross-compiled to 99% of known architectures
  4. Upon execution, the encrypted payload is written to the disk and immediately executed on the command line
  5. Alternatively, instead of a file-drop, it will execute the reconstitute shellcode in memory using amenzhinsky's go-memexec module github.com/amenzhinsky/go-memexec
  6. A custom shellcode executor is in the works, it takes ordinary C shellcode and after num-transform, it will run it by creating a new process after allocating the correct virtual address space and granting it RWX permissions on Windows

That means 32-bit, and 64-bit architectures, and it works on Linux, Windows, Macs, Unix, Android, iPhone, etc. You take, anything, and I mean ANYTHING, like the 1988 Morris Worm that nearly brought down the internet (which exploited a flaw in the fingerd listener daemon on UNIX), and make it a viable cyberweapon again.

EXOCET is designed to be used with the DSX Program, or the "Cyber Metal Gear" as I envisioned it. Being able to launch and proliferate dangerous malware without a traceable launch trail.

EXOCET is written entirely in Go.


How to use

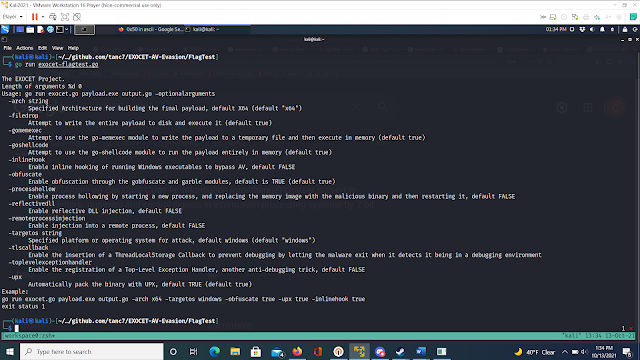
EXOCET, regardless of which binary you use to run it, requires Golang to work. By default, it generates a crypter .go file.

  1. Windows users: Install Go Here
  2. Linux users: run sudo apt-get update && sudo apt-get install -y golang
  3. You must install the EXOCET source files in golang go get github.com/tanc7/EXOCET-AV-Evasion
  4. Sub-requirements will also be downloaded and installed
  5. For Windows and Mac x64 Users, pre-compiled binaries are in the /bin folder

To run it

go run EXOCET.go detectablemalware.exe outputmalware.go

A key is automatically generated for you. The key is 64-characters long and is entirely composed of bash and cmd.exe shell pipe redirectors to confuse and disrupt brute-forcing attempts against the key by causing unpredictable, destructive behavior on the forensic analyst's device.

For 64-bit Windows Targets...

env GOOS=windows GOARCH=amd64 go build -ldflags "-s -w" -o outputMalware.exe outputmalware.go

And out comes a outputmalware.exe file

For 64-bit MacOS Targets

env GOOS=darwin GOARCH=amd64 go build -ldflags "-s -w" -o outputMalware.macho outputmalware.go

For 64-bit Linux Targets

env GOOS=linux GOARCH=amd64 go build -ldflags "-s -w" -o outputMalware.elf outputmalware.go

See this reference on github for your parameters for other operating systems like Android Reference for Go Cross Compilation

Note that the key can still be found with the strings command, please use the upx-ucl command to pack binary to conceal the key.

Furthermore, there are prebuilt binaries that I have made, meaning you just have to run ./EXOCET or EXOCET-Windows.exe


Legal Information

I, Chang Tan, and the creators of the main module and submodules of Exocet and the packages it incorporates are NOT responsible for the misuse of this tool. This is merely a penetration testing tool. You are strictly prohibited from deploying Exocet output binaries against unauthorized protected systems or unauthorized protected government systems.

I am aware that threat actors of APT41 and the NSO Group have used and/or adopted code from this tool, particularly the go-memexec method. If I were to be approached by Federal Investigators regarding the misuse of this tool, I am not claiming responsibility.

This is the same stuff that happened to the developers of Mimikatz and PowerShell Empire (who deprecated their own development upon realization of its use among threat actors). The successors have picked up development of Empire, and there are free alternatives such as Covenant C2.


EXOCET live demo
<iframe width="560" height="315" src="https://github.com/tanc7/EXOCET-AV-Evasion/blob/master/media/exocetdemo.mp4" frameborder="0" allow="accelerometer; autoplay; encrypted-media; gyroscope; picture-in-picture" allowfullscreen></iframe>
Reason for the name

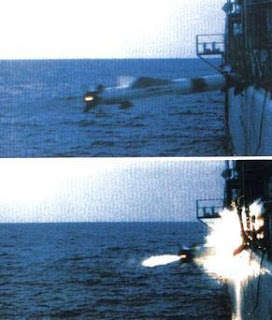
On May 4th, 1982, during the Falklands War, a squadron of Argentinan Super Eterdards launched a French made Exocet missile at the HMS Sheffield. Despite the Royal Navy's attempts to stop the missile, one struck, sinking the Sheffield. That incident literally put Argentina on the map as a show of force against a global colonial power.

News Article of the sinking of the HMS Sheffield

Very much like how Onel de Guzman's actions with the ILOVEYOU virus put the Philippines on the map as a cyber threat.

ILOVEYOU Virus on Wikipedia


Incoming update, notes and ambitions


So this month, and the next month is going to be a busy month for me, and there will be delays in implementing these methods. But I am excited to get started on implementing new AV evasion techniques such as...

  1. Inline hooking
  2. Obfuscation by emulating BlackRota and the gobfuscate module
  3. Process hollowing
  4. Reflective DLL injection
  5. Remote process injection
  6. ThreadLocalStorage Callbacks
  7. Registration of Top-Level Exception Handlers
  8. Custom UPX packing

I am a very busy man, I have the following priorities and I would like to request some help, some pull requests to aid in the project. Since I have the following things to do

  1. A court appearance in late October
  2. National Cyber League
  3. Accounting and Finance Classes, Computer Science was NEVER my college major and in the following weeks I will have exams back-to-back
  4. Federal Supervised Release Conditions and the FBI trying to implicate me in new unproven crimes. I have dash camera videos I uploaded to the cloud to prove it that I am sending to my lawyers. I have documented multiple attacks against me, vandalism of my car, my house, filed police reports and counter reports and will be building my case to file a Federal lawsuit. One of the perpetrators, who ripped out my front bumper of my car, has been arrested.
  5. A private project involving interaction with the CoinGeckoAPI
  6. Running the cryptoscopeinitiative.org, a to-be-filed 501c3 Non-Profit Organization
  7. Teaching three online classes on Exploit Development

Upcoming update! Direct encrypted shellcode execution! (Implemented in test versions, not released yet)

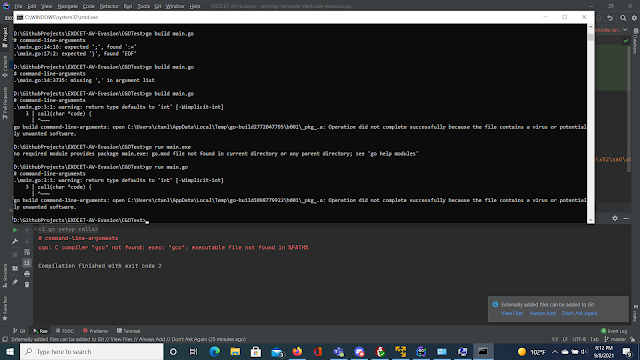
I need a bit of help, because I successfully implemented CGO to execute encrypted shellcode but it is throwing memory access violations exit status 0xc0000005. It shouldn't be anything related to DEP (Data Execution Prevention) because the file CGOTest/working-template-shellcode-executor.go did run.

Problem Discovered

As it turns out, VirtualAlloc must be called from kernel32.dll and ntdll.dll to properly make the memory page where the shellcode lands, readable, writable, and executable, in other word, set the PAGE_EXECUTE_READWRITE to ON. Read the Note on Memory Access Violation Problem below.


Once I figure this out, CGO was a pain in the ass to implement, we can now create crypters that execute INLINE-ASSEMBLY. Which was considered a impossibility until now.

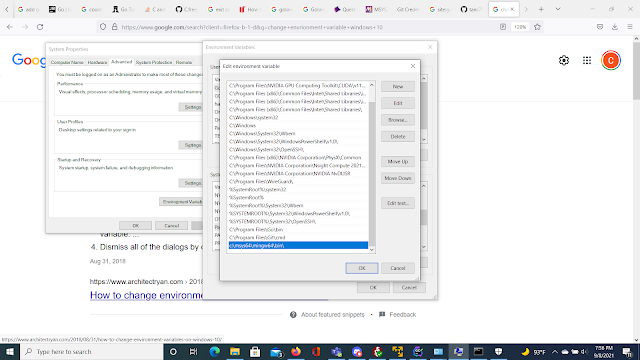
Note this requires Golang and the MinGW toolchain to be installed on Windows with you running and generating the shellcode on Windows. The reason why, is because CGO cannot be cross-compiled like our other EXOCET modules. To install the toolchain you need to go to https://www.msys2.org/ and follow the guide. Then you must add gcc to your environment variables in Windows

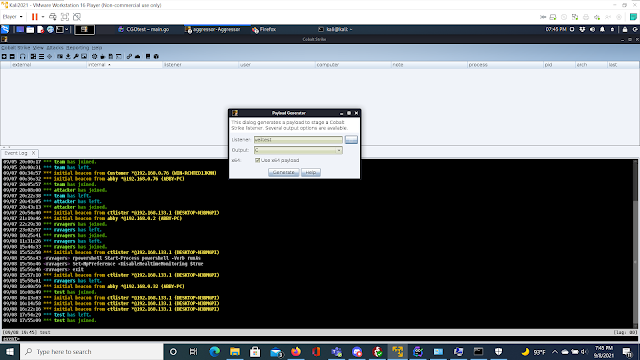
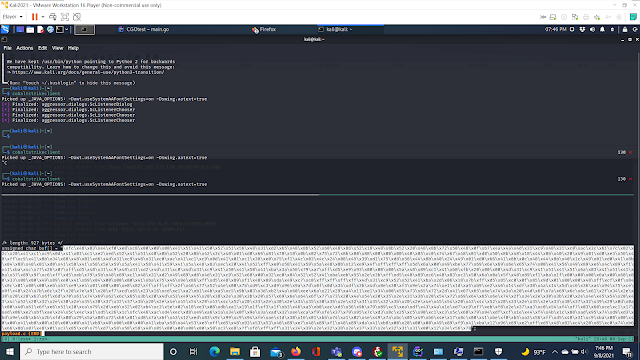
Step 1: Generate shellcode, this could be from msfvenom Meterpreter payloads, Cobalt Strike Beacons, or your own custom shellcode in C compatible format


Step 2: Copy only the bytes of the shellcode, excluding the quotes into a text file like sc.txt


Step 3: Your shellcode file should look like this. Raw shellcode


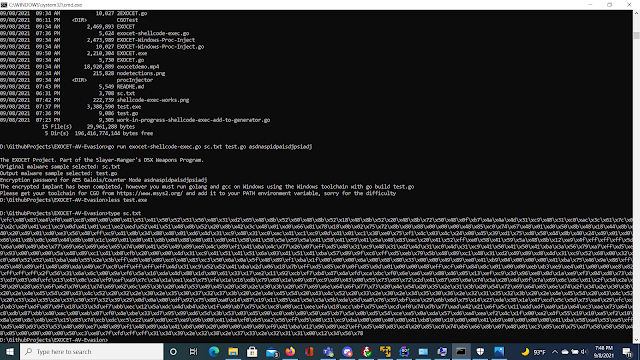
Step 4: Now run the command go run exocet-shellcode-exec.go sc.txt shellcodetest.go KEY

Step 5: You can attempt to run it but you'll run into memory access violation errors for some reason, which I am still working on


Note on Memory Access Violation Problem

Apparently, aside from the major limitations of CGO that prohibit or dramatically frustrates cross-compilation, the issue is that the shellcode we want to execute is landing in a section of memory (analyzed in WinDBG x64) that is not RWX. In other words, unless we write C code that explicitly allows execution in memory of the shellcode, it will always throw access violation errors.

The other method, that I observed other developers of rudimentary Go modules https://gist.github.com/mgeeky/bb0fd5652b234fbd1c7630d7e5c8542d, is that they use Go's Windows API to interact with ntdll.dll and kernel32.dll to call VirtualAlloc and specify areas of RWX memory pages. This method works better, but it seems that the shellcode must be in num-transformed format only for it to work.

I am still working on this you guys. I may combine multiple programming languages together to write a proper shellcode execution module


Note on Apple M1 Chips for precompiled binaries

Unfortunately I am running into errors for making a pre-compiled binary for MacBooks running the new M1 CPUs. It may be a issue with my Golang installation

â"Œâ"€â"€(rootðŸ'€kali)-[/opt/EXOCET-AV-Evasion]
â""â"€# GOOS=darwin GOARCH=arm64 go build exocet.go
# command-line-arguments
/usr/lib/go-1.15/pkg/tool/linux_amd64/link: running gcc failed: exit status 1
/tmp/go-link-477718799/go.o: file not recognized: file format not recognized
collect2: error: ld returned 1 exit status

Either way, you still require Golang to compile or cross-compile the malware to the platform you are targeting.


Related links